For security teams and MSSPs
Run a consistent, auditable pentest practice across your team.
PentestFlow Enterprise gives security leaders, MSSPs, and internal red teams the governance, traceability, and deployment options that procurement actually requires.
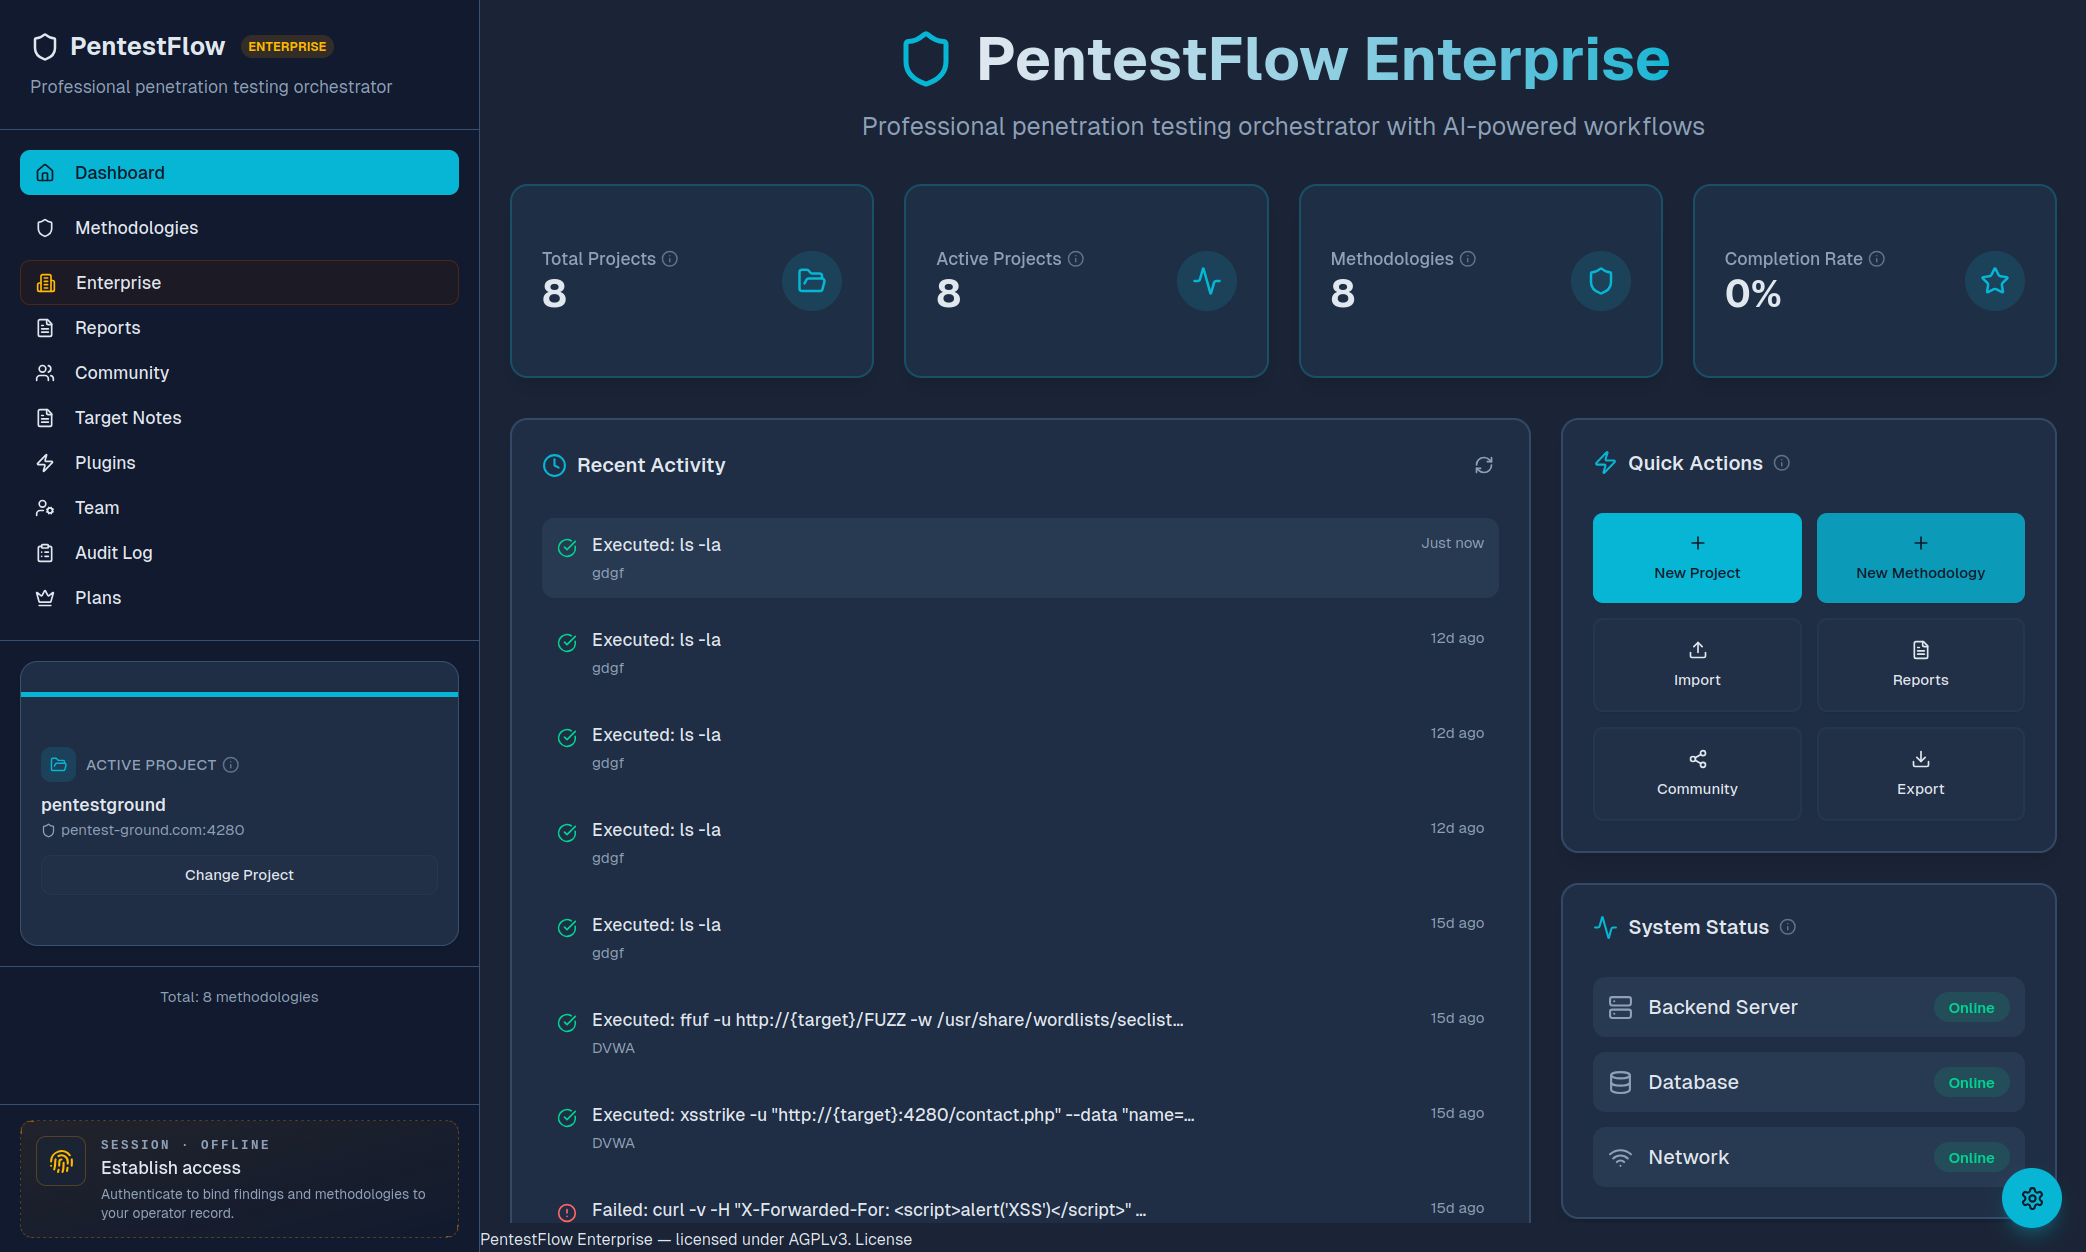
Teams and roles
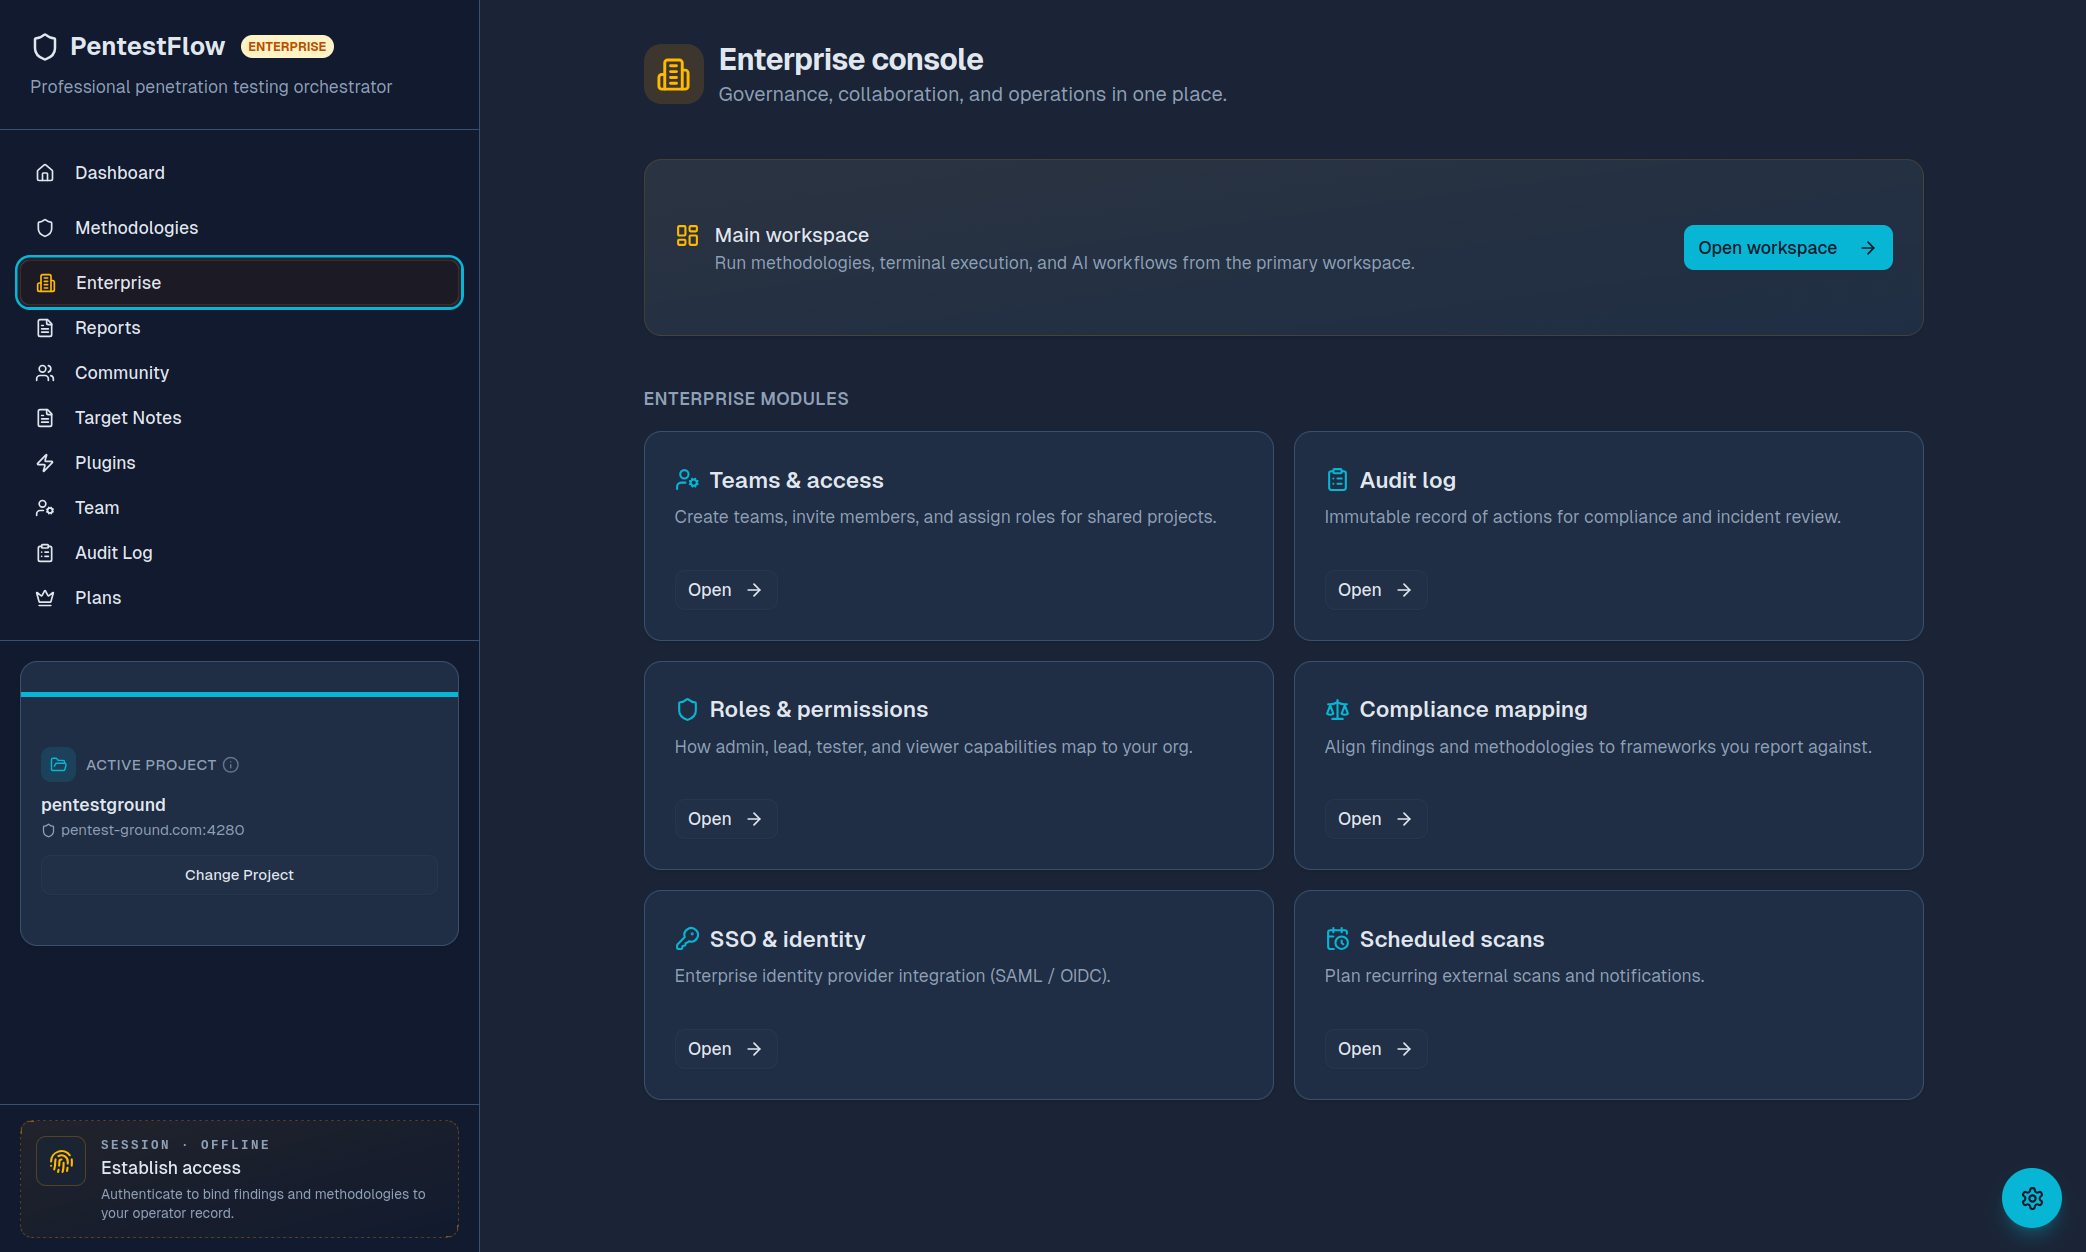
Invite testers, leads, and viewers. Assign engagements with project-level access and consistent process across clients.
Role-based access control
Granular permissions on projects, methodologies, evidence, and reports. Enforce who can run, view, or publish.
Audit log
Every meaningful action recorded with actor, target, and timestamp. Export to CSV for internal review or external audit.
SSO and SAML
Bring your identity provider. Enforce MFA at the IdP and centralize lifecycle management for your testers.
Scheduled scans
Recurring methodology runs against in-scope assets, with automatic evidence rollup and report generation.
Server-side PDF
Templated, branded PDF reports rendered server-side via WeasyPrint. Consistent output, no Word gymnastics.
Compliance mapping
Map findings and methodology steps to OWASP, NIST, PCI-DSS, and ISO 27001 controls (capability, not vendor certification).
Self-hosted by default
Docker, on-prem, or air-gapped deployment. Your evidence and reports stay inside your network.
One enterprise console
Teams, access, audit, and compliance in one place.
Trust by design
Your data does not leave your environment.
PentestFlow is engineered for self-hosted deployment from day one. Run it in Docker, on-prem, or fully air-gapped, with local-first AI and explicit policy controls on what tools can execute and where.
Read the trust centerLocal-first AI via Ollama, with optional cloud AI gated by tenant settings.
Execution policy: allowlist, blocklist, or unrestricted commands per environment.
Per-tenant isolation between projects, methodologies, and evidence.
Air-gap friendly: no required outbound network calls in the core workflow.
Ready to operationalize your pentest practice?
We will walk through your environment, scope, and procurement requirements, then put together a written proposal.